Secure Vibe Coding
Stay in Cursor or Claude — ship on Diode, not a public sandbox.
Consumer vibe platforms optimize for “anyone can demo an app.” Secure vibe coding on Diode Vibe is how teams and domain experts deploy those apps onto the Diode Network: agent-driven publish, static or container runtimes, and public / protected / private access — without babysitting ports or handing the workload to a shared public host.
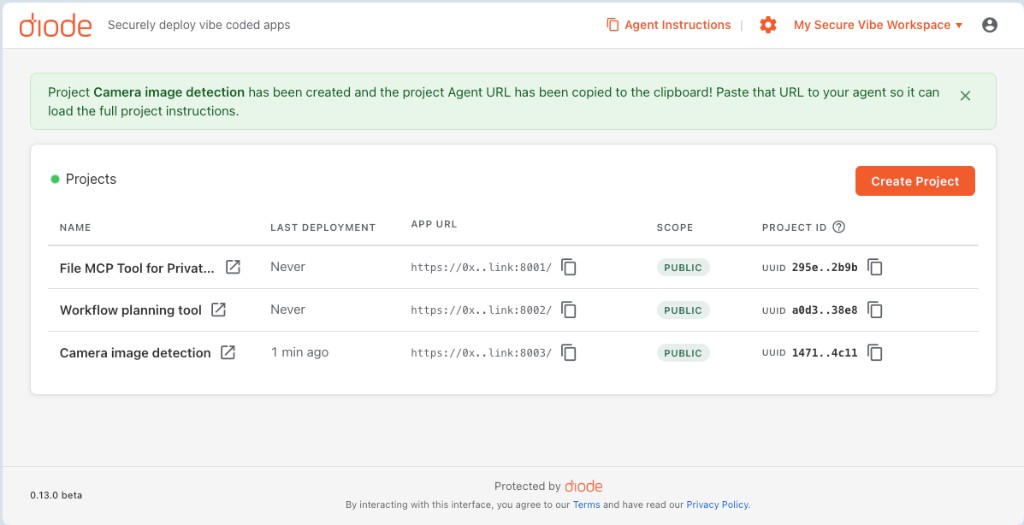
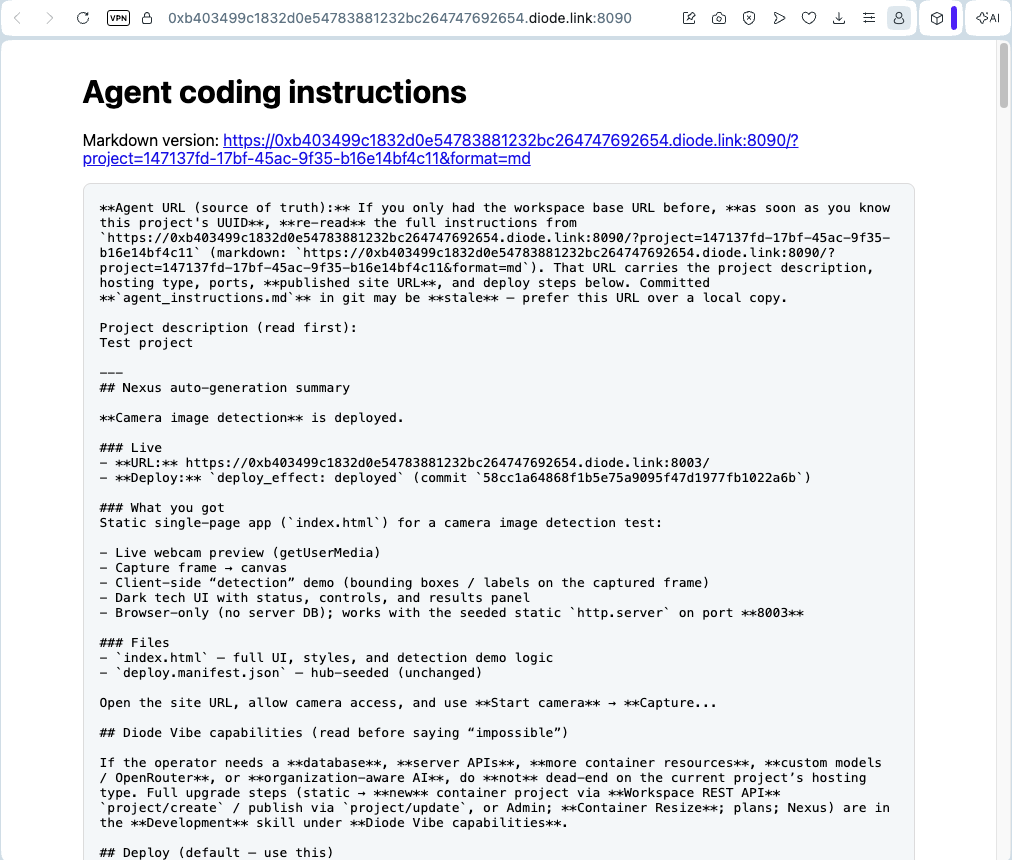
Paste an Agent URL into your coding tool. The agent packages, deploys, and polls logs. You keep working in the editor.
What this means
- Agent-driven deploy — Project-scoped Agent Instructions and HTTPS deploy (plus Automation API keys for CI and agents).
- Static and containers — HTML/CSS/JS sites, or Python/Node containers, published through Diode.
- Access you can defend — Public HTTPS when it should be open; protected or private when it should stay inside a Diode perimeter or Collab bookmark.
- Your hosting (Standard+) — Bring your own servers so runtimes live in your cloud, plant, or region.
- Your AI coding stack (Standard+) — Point the workspace at your Nexus so generation is organization-aware, not a hub default.
- Ops in the loop — Website monitoring, deploy history, and live Diode URLs.
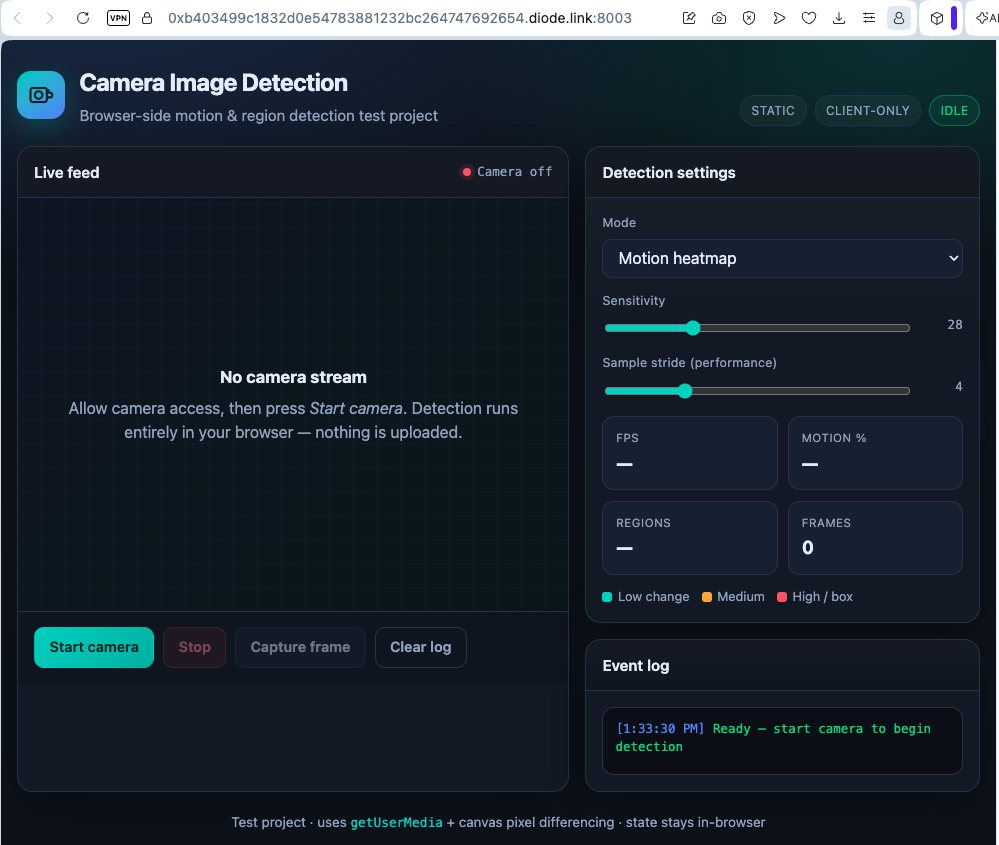
A published project is a real HTTPS app:
Advantages
- No SSH hop or public PaaS account required for the happy path
- Coding agents are first-class operators (instructions, deploy, logs)
- Same Diode identity and network as Collab, CLI, and Nexus
- Protected/private apps do not have to be “open on the internet to work”
- Grows from a static prototype to a container in the customer’s own environment
Applications
- Internal tools and dashboards that should not sit on a consumer vibe host
- Certification, attestation, and workflow apps built by domain experts
- Partner / supplier portals reached over Diode rather than a public SaaS
- Rapid prototypes that must already respect perimeter and residency
- Team workspaces where Owners/Admins control publish scope and hosts